
Introduction to PCI Compliance
What is PCI Compliance?
PCI Compliance refers to the Payment Card Industry Data Security Standard (PCI DSS), a set of security standards designed to ensure that all companies that accept, process, store, or transmit credit card information maintain a secure environment. This standard applies to any entity involved in payment card processing, including merchants, processors, acquirers, issuers, and service providers, regardless of their size or transaction volume.
Secure Your Business with Tide Networks
Ensuring PCI compliance is essential for safeguarding your customers’ payment information and maintaining their trust. Tide Networks is here to assist you in navigating the complexities of PCI DSS, offering expert advice, and implementing effective security measures. Contact us today to learn more about how we can help your business achieve and maintain PCI compliance, ensuring a secure and trustworthy environment for your customers.
The Importance of PCI Compliance
Why Your Business Needs to be PCI Compliant
Achieving PCI compliance is crucial for businesses that handle credit card information. It not only helps in avoiding potential fines and penalties associated with non-compliance but also plays a significant role in protecting sensitive cardholder data against breaches and theft. Compliance demonstrates to your customers that you are committed to maintaining a secure environment for their transactions, thereby building trust and loyalty.
Levels of PCI Compliance
Understanding the Different Levels of PCI Compliance
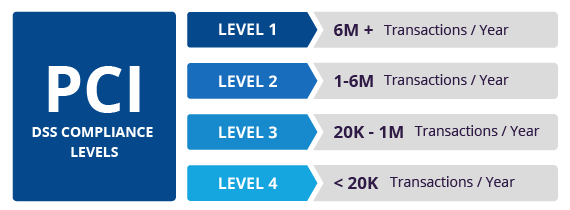
- Level 1: Applies to merchants processing over 6 million transactions annually or those identified by Visa/Mastercard as needing to meet Level 1 requirements.
- Level 2: For merchants processing between 1 million and 6 million transactions annually.
- Level 3: E-commerce merchants processing 20,000 to 1 million transactions annually.
- Level 4: E-commerce merchants processing fewer than 20,000 transactions annually or other merchants processing fewer than 1 million transactions.
PCI Compliance Checklist
12 Key Requirements for PCI Compliance
- Implement and maintain a firewall configuration to protect cardholder data.
- Do not use vendor-supplied defaults for system passwords and other security parameters.
- Protect stored cardholder data.
- Encrypt transmission of cardholder data across open, public networks.
- Protect all systems against malware and regularly update antivirus software or programs.
- Develop and maintain secure systems and applications.
- Restrict access to cardholder data by business need to know.
- Assign a unique ID to each person with computer access.
- Restrict physical access to cardholder data.
- Track and monitor all access to network resources and cardholder data.
- Regularly test security systems and processes.
- Maintain a policy that addresses information security for all personnel.
How Tide Networks Can Help
Partnering with Tide Networks for PCI Compliance
Tide Networks offers comprehensive services to help your business achieve and maintain PCI compliance. From initial assessment to implementing security measures and ongoing support, our team of experts is equipped to guide you through each step of the compliance process. We understand the unique challenges businesses face in meeting PCI DSS requirements and are committed to providing tailored solutions that not only ensure compliance but also enhance your overall security posture.
Contact us today!
Contact Us
(813) 308-9062
Serving Tampa Bay
Monday-Friday: 8am - 5pm